為什麼選擇 OpenText
為什麼選擇 OpenText
概述為什麼選擇 OpenText
OpenText 擁有數十年的專業知識,可幫助您釋放資料、連結人員和流程,並以信任推動 AI
管理和連結資料
在您的企業中無縫統一資料,消除孤島、改善協作並降低風險
具備 AI 的資訊
做好 AI 準備,並將您的資料轉化為結構化、可存取且優化的資訊
內建的安全性與合規性
滿足法規和合規要求,並讓資訊在整個生命週期中受到保護
AI 領導力
概述Aviator AI
以全新的方式查看資訊
OpenText™ Aviator™
AI 了解您的企業、您的資料與您的目標
OpenText™ Content Aviator™
利用 AI 內容管理和智能 AI 內容助手提升工作效率
OpenText™ Service Management Aviator™
賦能使用者、服務代理和 IT 人員,讓他們找到所需的答案
OpenText™ Software Delivery Aviator™
加快應用程式的交付、開發和自動化軟體測試
OpenText™ Trading Grid™ Aviator™
解鎖貫穿整個供應鏈的 AI 驅動知識、洞察力與引導式行動
Aviator AI
概述Aviator AI
以全新的方式查看資訊
OpenText™ Aviator™
AI 了解您的企業、您的資料與您的目標
OpenText™ Content Aviator™
利用 AI 內容管理和智能 AI 內容助手提升工作效率
OpenText™ Service Management Aviator™
賦能使用者、服務代理和 IT 人員,讓他們找到所需的答案
OpenText™ Software Delivery Aviator™
加快應用程式的交付、開發和自動化軟體測試
OpenText™ Trading Grid™ Aviator™
解鎖貫穿整個供應鏈的 AI 驅動知識、洞察力與引導式行動
商業網路
概述Business Network
只需連結一次,即可透過安全的 B2B 整合平台觸及任何目標
內容
概述Content
以具備 AI 的內容管理解決方案重新構想知識
應用交付管理
概述Application Delivery Management
利用 AI 驅動的 DevOps 自動化、測試和品質,更快速交付更優質的軟體
可觀察性與服務管理
概述Observability and Service Management
獲得所需的清晰度,以降低 IT 營運的成本和複雜性
API
概述APIs
透過建置整合功能、自動化流程及客製化體驗,充分發揮您的 OpenText 解決方案的價值
OpenText™ API Services
使用 OpenText Cloud API 按照您的方式構建,創建支持自訂應用程式和工作流程的即時資訊流
可信資料與 AI
概述可信資料與 AI
安全資訊管理與可信賴的 AI 相遇
OpenText™ Aviator™ Studio
一個可以使用資料語言建置、部署和迭代代理程式的地方
OpenText™ Discovery
一套用於幫助擷取資料和自動添加元資料標記的工具,以推動 AI 發展
OpenText™ Data Compliance
一套服務和 API,使治理變得主動且持久
OpenText™ Aviator™ AI Services
專業服務專家協助您踏上 AI 旅程
人工智能
概述Aviator AI
以全新的方式查看資訊
OpenText™ Aviator™
AI 了解您的企業、您的資料與您的目標
OpenText™ Content Aviator™
利用 AI 內容管理和智能 AI 內容助手提升工作效率
OpenText™ Service Management Aviator™
賦能使用者、服務代理和 IT 人員,讓他們找到所需的答案
OpenText™ Software Delivery Aviator™
加快應用程式的交付、開發和自動化軟體測試
OpenText™ Trading Grid™ Aviator™
解鎖貫穿整個供應鏈的 AI 驅動知識、洞察力與引導式行動

代理式應用程式安全性
透過 Fortify Agentic Analyzer,找出基於規則的分析無法發現的內容
概述

主要優點
在不離開您現有 Fortify 工作流程的情況下,找出基於規則的分析遺漏的弱點。
-

找出基於規則的分析無法觸及的關鍵漏洞
代理式分析在 10 種語言中可捕捉 12 個真實重大 CVE 漏洞中的 10 個,其中多數的 CVSS 評分為 9.0 或更高 — 這些漏洞多為缺乏可追蹤的受污染資料路徑的邏輯和授權漏洞。
-

在同一處管理所有發現項目
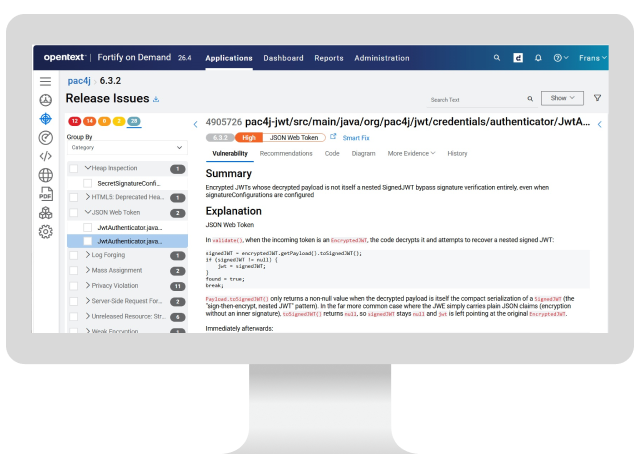
結果會與您以基於規則的分析取得的 SAST 結果進行去重比對,對應至 Fortify 類別,並顯示於 Fortify Software Security Center 和 Fortify on Demand 中。無需第二個工具,也無需第二個分流佇列。
-

無需新增 SKU,即可拓展代理式能力
Fortify Agentic Analyzer 已包含於您現有的 Fortify SAST 授權中。自備來自任何受支援提供商的 LLM,且僅需針對使用量向您的提供商付費。
商業影響
-
邏輯與授權缺陷偵測
有些漏洞不會留下可供追蹤的資料軌跡。清除誤報(例如被誤認為寫死密碼的訊息字串),並找出基於規則的分析無法追蹤的邏輯和授權漏洞。
-
為高風險應用程式提供更深入的涵蓋範圍
定期於關鍵應用程式上執行代理式分析,就像排定滲透測試一樣,而 SAST 則持續作為快速和每日進行的第一道防線。
-
僅限全新發現項目
團隊在重新分流 SAST 已發現的問題時,往往會耗費許多時間。將您的 SAST 分析結果上傳後,Fortify Agentic Analyzer 便會自動過濾掉重複項目,讓您的團隊僅需審查真正的新內容。
-
單一記錄系統
發現項目會以 Fortify 分類法呈現於 Fortify Software Security Center 和 Fortify on Demand 中,且可匯出為 SARIF,因此代理式分析結果會與您 AppSec 計畫中的其他結果一同呈現。
-
掃描成本控管
您可自備 LLM,以便自行掌控支出。設定每次執行的費用上限,為各階段選擇模型和投入程度,並於關鍵應用程式上進行更深入的分析,在其他應用程式上則採取較輕量的分析。
探索解決方案的各個組成部分
產品
OpenText 將代理式分析和基於規則的分析整合至單一應用程式安全性計畫中。Fortify Agentic Analyzer(隨 SAST 一併提供)可找出基於規則的分析無法發現的內容;Fortify SAST 提供快速且具確定性的涵蓋能力;Fortify on Demand 則以 SaaS 形式提供上述功能。
- OpenText™ Fortify™ SAST及早發現並修正安全問題,以業界領先的準確度
- OpenText™ Fortify™ Remediation Aviator™利用人工智慧,從噪音中獲取結果,該人工智慧不僅能指出缺陷,還能顯示程式碼修復方案。
- OpenText™ Fortify™ on Demand解鎖安全測試、漏洞管理,以及量身打造的專業知識與支援
- 企業應用程式安全平台賦能開發人員,加強安全性,加快交付速度。
Resources
-
Agentic AST is the category Gartner defines for AI-agent-driven code analysis. Rather than matching rules or tracing a data path, AI agents reason about your source code the way an expert reviewer would, following logic and intent to find vulnerabilities rules-based analysis can't reach. Fortify Agentic Analyzer applies this to your codebase to uncover flawed authorization design, business-logic weaknesses, and subtle injection and persistence patterns. It complements Fortify SAST, which runs a suite of deterministic analyzers fast enough to use on every build.
-
No. It complements SAST, it does not replace it. Fortify SAST stays your fast, broad, deterministic first line of defense on every build, covering a wide range of weakness classes. Fortify Agentic Analyzer adds a deeper, agentic pass you run selectively on higher-risk applications, the way you would schedule a penetration test. Used together, they cover ground neither reaches alone.
-
Yes. It is included under your existing Fortify SAST license at no additional charge. If an application is licensed for SAST analysis, you can analyze it with agentic analysis too, whether you connect through Fortify Software Security Center or Fortify on Demand. You bring your own LLM and pay your provider for usage: there is no separate SKU and no fixed AI surcharge from OpenText.
-
The flaws that turn on logic and intent rather than a traceable data path: broken authorization and authentication design, business-logic weaknesses, and subtle injection and persistence patterns. In a published study across 10 languages, Fortify Agentic Analyzer found 10 of 12 real-world CVEs, most rated CVSS 9.0 or higher, all disclosed after the analysis model's training cutoff, so the results reflect reasoning about the code rather than recall of a known bug.
-
You bring your own. Fortify Agentic Analyzer works with a wide set of LLM providers, connected through your own API key or a supported subscription, so you control model choice and cost. Usage is billed by your provider, not by OpenText. You can select the model and effort level for each stage of a scan to balance depth against spend.
-
They are distinct Fortify capabilities. Fortify Agentic Analyzer finds vulnerabilities rules-based analysis can't reach. Fortify Remediation Aviator triages findings and generates fixes to speed remediation. Fortify Agentic Analyzer does not require Remediation Aviator (which is an add-on). Fortify Agentic Analyzer is included with Fortify SAST.
-
Findings appear in Fortify Software Security Center and Fortify on Demand, reported in the Fortify taxonomy alongside your SAST, DAST, and SCA results, so agentic findings live in the same system of record your team already uses. Findings are deduplicated against your existing SAST results, so you review only what's net-new, and output is also available as SARIF for downstream tools.
-
Because you bring your own LLM, you control the spend. Set a per-run cost cap, choose the model and effort level for each stage, and run agentic analysis where it earns its keep: deeper on your critical applications, lighter elsewhere. There is no fixed AI surcharge from OpenText on top of your provider usage.


