为什么选择 OpenText
为什么选择 OpenText
概述为什么选择 OpenText
OpenText 拥有数十年的专业经验,可帮助您解锁数据、连接人员和流程,并以信任为 AI 提供动力
AI 领导力
概述Aviator AI
以全新方式查看信息
OpenText™ Aviator™
能够理解您的业务、数据和目标的 AI
OpenText™ Content Aviator™
利用 AI 内容管理和智能 AI 内容助手实现高效工作
OpenText™ Service Management Aviator™
让用户、服务代理和 IT 人员能够找到他们所需的答案
OpenText™ Software Delivery Aviator™
实现更快的应用交付、开发和自动化软件测试
OpenText™ Trading Grid™ Aviator™
在整个供应链中解锁 AI 驱动的知识、洞察与引导式行动
Aviator AI
概述Aviator AI
以全新方式查看信息
OpenText™ Aviator™
能够理解您的业务、数据和目标的 AI
OpenText™ Content Aviator™
利用 AI 内容管理和智能 AI 内容助手实现高效工作
OpenText™ Service Management Aviator™
让用户、服务代理和 IT 人员能够找到他们所需的答案
OpenText™ Software Delivery Aviator™
实现更快的应用交付、开发和自动化软件测试
OpenText™ Trading Grid™ Aviator™
在整个供应链中解锁 AI 驱动的知识、洞察与引导式行动
商业网络
概述Business Network
一次连接,即可通过安全的 B2B 集成平台触达一切
DevOps
概述DevOps
通过 AI 驱动的 DevOps 自动化、测试和质量,更快地交付更优质的软件
可观测性和服务管理
概述Observability and Service Management
获得所需的清晰度,以降低 IT 运营的成本和复杂性
API
概述APIs
通过构建集成、自动化,以及定制化体验,进一步提升 OpenText 解决方案的价值
OpenText™ API Services
使用 OpenText 云 API 按自己的方式构建,这些 API 可创建实时信息流,从而支持自定义应用程序和工作流
可信数据与 AI
概述可信数据与 AI
安全信息管理与可信的 AI 相结合
OpenText™ Aviator™ Studio
在这里,您可以使用数据语言构建、部署和迭代代理
OpenText™ Discovery
一套用于帮助摄取数据和自动化元数据标记,以推动 AI 发展的工具
OpenText™ Data Compliance
一套使治理具有主动性和持久性的服务和 API
OpenText™ Aviator™ AI Services
专业服务专家助您踏上 AI 之旅
人工智能
概述Aviator AI
以全新方式查看信息
OpenText™ Aviator™
能够理解您的业务、数据和目标的 AI
OpenText™ Content Aviator™
利用 AI 内容管理和智能 AI 内容助手实现高效工作
OpenText™ Service Management Aviator™
让用户、服务代理和 IT 人员能够找到他们所需的答案
OpenText™ Software Delivery Aviator™
实现更快的应用交付、开发和自动化软件测试
OpenText™ Trading Grid™ Aviator™
在整个供应链中解锁 AI 驱动的知识、洞察与引导式行动

智能体应用安全
使用 Fortify Agentic Analyzer,发现基于规则的分析无法发现的内容
概述

主要优势
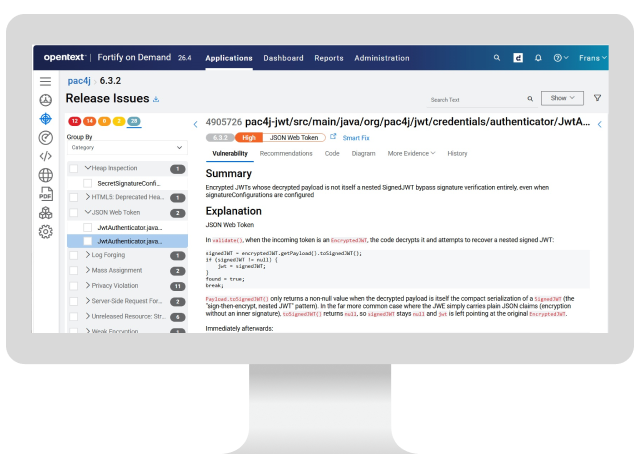
无需离开您当前使用的 Fortify 工作流,即可发现基于规则的分析所遗漏的漏洞。
-

发现基于规则的分析无法检测到的关键漏洞
智能体分析可跨 10 种语言捕获 12 个真实严重 CVE 中的 10 个,其中大多数被评为 CVSS 9.0 或更高级别——这些逻辑和授权漏洞不存在可追踪的受污染数据路径。
-

在一个位置管理所有发现结果
调查结果会与您基于规则的 SAST 结果进行去重,映射到 Fortify 类别,并显示在 Fortify Software Security Center 和 Fortify on Demand 中。无需第二种工具,也无需第二个分诊队列。
-

无需新增 SKU,深化智能体能力
Fortify Agentic Analyzer 已包含在您现有的 Fortify SAST 许可证中。您可以接入任何受支持提供商的 LLM,使用费用仅需支付给该提供商。
商业影响
-
逻辑和授权缺陷检测
有些漏洞没有可供追踪的数据痕迹。清除误报,例如将消息字符串误认为硬编码密码的情况,并揭示基于规则的分析无法追踪的逻辑和授权漏洞。
-
为高风险应用提供更深层次的覆盖
定期对您的关键应用运行智能体分析,就像安排渗透测试一样,同时让 SAST 继续作为您快速、日常的第一道防线。
-
仅限全新发现结果
团队浪费时间重新分诊 SAST 已经发现的问题。将您的 SAST 结果传入 Fortify Agentic Analyzer,它会剔除重复项,让您的团队只审核新增内容。
-
单一权威记录系统
调查结果会以 Fortify 分类体系呈现在 Fortify Software Security Center 和 Fortify on Demand 中,并可导出为 SARIF,因此智能体分析结果可与 AppSec 计划的其余内容并存。
-
扫描成本控制
您使用自己的 LLM,因此可以掌控成本。 设置每次运行的费用上限,为每个阶段选择模型和分析力度,并在关键应用上进行更深入的分析,在其他应用上则采用较轻量的分析
探索解决方案的组成部分
产品
OpenText 将智能体分析与基于规则的分析整合到一个应用程序安全计划中。 Fortify Agentic Analyzer(随 SAST 一同提供)可发现基于规则的分析无法发现的内容;Fortify SAST 提供快速、确定性的覆盖;Fortify on Demand 则以 SaaS 形式交付。
- OpenText™ Fortify™ SAST以行业领先的准确性,尽早发现并修复安全问题
- OpenText™ Fortify™ Remediation Aviator™利用 AI 技术从干扰中获取结果——既能揭示缺陷,也能显示代码修复情况
- OpenText™ Fortify™ on Demand解锁安全测试、漏洞管理以及量身定制的专业知识与支持
- 企业应用程序安全平台赋能开发人员,强化安全措施,加快交付流程
Resources
-
Agentic AST is the category Gartner defines for AI-agent-driven code analysis. Rather than matching rules or tracing a data path, AI agents reason about your source code the way an expert reviewer would, following logic and intent to find vulnerabilities rules-based analysis can't reach. Fortify Agentic Analyzer applies this to your codebase to uncover flawed authorization design, business-logic weaknesses, and subtle injection and persistence patterns. It complements Fortify SAST, which runs a suite of deterministic analyzers fast enough to use on every build.
-
No. It complements SAST, it does not replace it. Fortify SAST stays your fast, broad, deterministic first line of defense on every build, covering a wide range of weakness classes. Fortify Agentic Analyzer adds a deeper, agentic pass you run selectively on higher-risk applications, the way you would schedule a penetration test. Used together, they cover ground neither reaches alone.
-
Yes. It is included under your existing Fortify SAST license at no additional charge. If an application is licensed for SAST analysis, you can analyze it with agentic analysis too, whether you connect through Fortify Software Security Center or Fortify on Demand. You bring your own LLM and pay your provider for usage: there is no separate SKU and no fixed AI surcharge from OpenText.
-
The flaws that turn on logic and intent rather than a traceable data path: broken authorization and authentication design, business-logic weaknesses, and subtle injection and persistence patterns. In a published study across 10 languages, Fortify Agentic Analyzer found 10 of 12 real-world CVEs, most rated CVSS 9.0 or higher, all disclosed after the analysis model's training cutoff, so the results reflect reasoning about the code rather than recall of a known bug.
-
You bring your own. Fortify Agentic Analyzer works with a wide set of LLM providers, connected through your own API key or a supported subscription, so you control model choice and cost. Usage is billed by your provider, not by OpenText. You can select the model and effort level for each stage of a scan to balance depth against spend.
-
They are distinct Fortify capabilities. Fortify Agentic Analyzer finds vulnerabilities rules-based analysis can't reach. Fortify Remediation Aviator triages findings and generates fixes to speed remediation. Fortify Agentic Analyzer does not require Remediation Aviator (which is an add-on). Fortify Agentic Analyzer is included with Fortify SAST.
-
Findings appear in Fortify Software Security Center and Fortify on Demand, reported in the Fortify taxonomy alongside your SAST, DAST, and SCA results, so agentic findings live in the same system of record your team already uses. Findings are deduplicated against your existing SAST results, so you review only what's net-new, and output is also available as SARIF for downstream tools.
-
Because you bring your own LLM, you control the spend. Set a per-run cost cap, choose the model and effort level for each stage, and run agentic analysis where it earns its keep: deeper on your critical applications, lighter elsewhere. There is no fixed AI surcharge from OpenText on top of your provider usage.


