OpenTextが選ばれる理由
OpenTextが選ばれる理由
概要OpenTextが選ばれる理由
OpenTextは数十年の専門知識を提供し、データのロックを解除し、人々とプロセスをつなぎ、信頼性を持ってAIを推進
データを管理し、接続する
企業全体でデータをシームレスに統合し、サイロを排除し、コラボレーションを改善し、リスクを軽減
AI対応情報
AIに対応し、データを構造化され、アクセスしやすく、最適化された情報に変換
組み込みのセキュリティとコンプライアンス
規制およびコンプライアンス要件を満たし、情報のライフサイクル全体を保護
どこでも展開可能
概要導入オプション
あらゆる規模のグローバル組織に対応するスケーラブルで柔軟な導入オプションを探る
主権クラウド
ローカルなコントロール、グローバルなスケールで信頼できるAIを活用。
プライベートクラウド
コントロールとコンプライアンスを維持しながら、クラウドの価値を引き出します。
オンプレミス
自社インフラストラクチャでデータを完全に管理
パブリッククラウド
選択したクラウドでビジネス情報を保護、拡張、利用
AIリーダーシップ
概要Aviator AI
新しい方法で情報を捉える
OpenText™ Aviator™
ビジネス、データ、目標を理解するAI
OpenText™ Content Aviator™
AIコンテンツ管理とインテリジェントなAIコンテンツアシスタントで業務を強化
OpenText™ Service Management Aviator™
ユーザー、サービスエージェント、ITスタッフが必要な答えを見つけられるように支援
OpenText™ Software Delivery Aviator™
アプリの配信、開発、自動化されたソフトウェアテストの加速を実現
OpenText™ Trading Grid™ Aviator™
サプライチェーン全体でAIを活用したナレッジ、インサイト、およびガイド付きアクションを引き出す
Aviator AI
概要Aviator AI
新しい方法で情報を捉える
OpenText™ Aviator™
ビジネス、データ、目標を理解するAI
OpenText™ Content Aviator™
AIコンテンツ管理とインテリジェントなAIコンテンツアシスタントで業務を強化
OpenText™ Service Management Aviator™
ユーザー、サービスエージェント、ITスタッフが必要な答えを見つけられるように支援
OpenText™ Software Delivery Aviator™
アプリの配信、開発、自動化されたソフトウェアテストの加速を実現
OpenText™ Trading Grid™ Aviator™
サプライチェーン全体でAIを活用したナレッジ、インサイト、およびガイド付きアクションを引き出す
Business Network
概要Business Network
一度接続するだけで、安全なB2B統合プラットフォームからすべてに連携
Content
概要Content
AI対応のコンテンツ管理ソリューションで知識を再構築
サイバーセキュリティ
概要Cybersecurity
企業保護のための統合サイバーセキュリティソリューション
アプリケーション配信管理
概要Application Delivery Management
AIを活用したDevOpsの自動化、テスト、品質向上により、より優れたソフトウェアをより迅速に提供
オブザーバビリティとサービス管理
概要Observability and Service Management
IT運用のコストと複雑さを削減するために必要な明確性を獲得
API
概要APIs
統合、自動化、カスタムエクスペリエンスを構築して、OpenTextのソリューションを最大限にご利用ください
OpenText™ API Services
カスタムアプリケーションとワークフローを可能にするリアルタイムな情報フローを作成するOpenText Cloud APIを使用して、お客様独自の方法で構築
信頼できるデータとAI
概要信頼できるデータとAI
安全な情報管理と信頼できるAIの融合
OpenText™ Aviator™ Studio
データ言語でエージェントを構築、デプロイ、反復できる場所
OpenText™ Discovery
AIを促進するためのデータ取り込みとメタデータタグ付けを自動化するツールセット
OpenText™ Data Compliance
ガバナンスを積極的かつ持続的にするためのサービスとAPIのスイート
OpenText™ Aviator™ AI Services
AIのジャーニーをサポートするプロフェッショナルサービスのエキスパート
情報の再構築
概要情報の再構築
AIを活用した情報管理により、可視性が向上し、より鮮明な洞察が得られます。その方法を確認する準備はよろしいですか?
ナレッジの再構築
AIを活用したエンタープライズコンテンツ管理で日常業務を変革する
サービス管理の再構築
ITサービス管理、AIOps、可観測性のコストと複雑さを削減
つながりの再構築
サプライチェーン成功のためのAIを活用したB2B統合
会話の再構築
コネクテッドカスタマーエクスペリエンスで価値、成長、ロイヤルティを向上
エンジニアリングの再構築
アジャイル開発とソフトウェアデリバリー?決して不可能ではありません。
セキュリティの再構築
エンタープライズ向けサイバーセキュリティ
意思決定の再構築
AIデータ分析で洞察を引き出す
人工知能
概要Aviator AI
新しい方法で情報を捉える
OpenText™ Aviator™
ビジネス、データ、目標を理解するAI
OpenText™ Content Aviator™
AIコンテンツ管理とインテリジェントなAIコンテンツアシスタントで業務を強化
OpenText™ Service Management Aviator™
ユーザー、サービスエージェント、ITスタッフが必要な答えを見つけられるように支援
OpenText™ Software Delivery Aviator™
アプリの配信、開発、自動化されたソフトウェアテストの加速を実現
OpenText™ Trading Grid™ Aviator™
サプライチェーン全体でAIを活用したナレッジ、インサイト、およびガイド付きアクションを引き出す
サービス内容
概要サービス内容
認定エキスパートによるガイダンスでデジタルトランスフォーメーションを加速
プロフェッショナルサービス
認定専門家と連携して情報管理を近代化
カスタマーサクセスサービス
専門家のガイダンス、マネージド サービスなどを活用してビジネス目標を達成
サポートサービス
サポートを戦略的優位性に変える
Managed Services
専門的なITサービス管理で社内チームの負担を軽減
ラーニングサービス
あらゆるスキルレベルのユーザーがOpenText製品を導入し、効果的に使用できるようにするためのトレーニングオプションをご紹介します。
ラーニングサービス
概要ラーニングサービス
あらゆるスキルレベルのユーザーがOpenText製品を導入し、効果的に使用できるようにするためのトレーニングオプションをご紹介します。

クラウドパートナー
概要クラウドパートナー
OpenTextは、主要なクラウドインフラストラクチャプロバイダーと提携し、OpenTextソリューションをどこでも実行できる柔軟性を提供します。
エンタープライズアプリケーションパートナー
概要エンタープライズアプリケーションパートナー
OpenTextは主要エンタープライズアプリプロバイダーと提携し、非構造化コンテンツを活用してビジネスインサイトを向上
地域を選択してください:
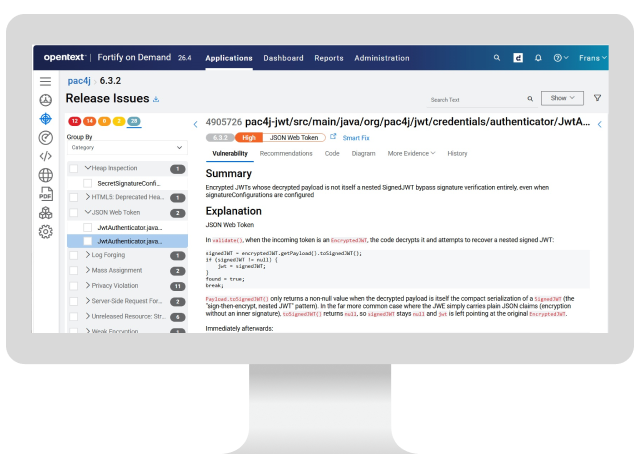
エージェント型アプリケーションセキュリティ
Fortify Agentic Analyzerで、ルールベースの分析では検出できない問題を発見
概要

主なメリット
既存のFortifyワークフローを離れることなく、ルールベースの分析では見逃される脆弱性を検出します。
-

ルールベースの分析では検出できない重大な欠陥を発見
エージェント型分析は、10言語にわたり、実際の重大なCVE 12件のうち10件を検出します。その大半はCVSS 9.0以上と評価された、追跡すべき汚染データパスが存在しないロジックや認可のバグです。
-

すべての調査結果を1か所で管理
検出結果は、ルールベースのSAST結果と照合して重複が排除され、Fortifyのカテゴリにマッピングされたうえで、Fortify Software Security CenterおよびFortify on Demandに表示されます。 別のツールや、別のトリアージキューは必要ありません。
-

新しいSKUを追加することなく、エージェント性を深める
Fortify Agentic Analyzerは、既存のFortify SASTライセンスに含まれています。 サポートされている任意のプロバイダーから独自のLLMを持ち込むことができ、お支払いはプロバイダーへの利用料金のみです。
ビジネスへの影響
-
ロジックと認可の脆弱性を検知
追跡できるデータの痕跡が残らない欠陥もあります。 メッセージ文字列がハードコードされたパスワードと誤認されるような誤検知を解消し、ルールベースの分析では追跡できないロジックや認可の欠陥を明らかにします。
-
高リスクアプリをより深く網羅
SASTを日々の迅速な第一防衛線として維持しながら、ペネトレーションテストをスケジュールするのと同じように、重要なアプリでエージェント型分析を定期的に実行してください。
-
新たな検出結果のみ
チームは、SASTがすでに検出した問題を再トリアージすることに時間を浪費しています。 SASTの結果を渡せば、Fortify Agentic Analyzerがそれらを除外するため、チームは純粋に新規の項目のみをレビューできます。
-
レコードを保存する単一のシステム
検出結果はFortifyの分類体系に基づいてFortify Software Security CenterおよびFortify on Demandに取り込まれ、SARIF形式でエクスポートされるため、AIエージェントによる結果をアプリケーションセキュリティプログラムの他の結果と並べて管理できます。
-
スキャンコスト管理
独自のLLMを使用することで、支出を管理できます。 実行ごとのコスト上限を設定し、各ステージのモデルと分析の強度を選択して、重要なアプリではより詳細に、その他ではより軽めに分析してください。
ソリューションの構成要素を探る
製品
OpenTextは、エージェント型分析とルールベースの分析を1つのアプリケーションセキュリティプログラムに統合します。Fortify Agentic Analyzer(SASTに付属)は、ルールベースの分析では検出できないものを発見します。Fortify SASTは高速かつ決定論的なカバレッジを提供し、Fortify on DemandはそれをSaaSとして提供します。
- OpenText™ Fortify™ SAST業界トップクラスの精度でセキュリティ問題を早期に発見・修正
- OpenText™ Fortify™ Remediation Aviator™欠陥だけでなくコード修正も表示するAIを活用して、ノイズから成果へと移行
- OpenText™ Fortify On Demandセキュリティテスト、脆弱性管理、カスタマイズされた専門知識とサポートの提供
- エンタープライズアプリケーションセキュリティプラットフォーム開発者を支援し、セキュリティを強化し、デリバリーを加速化。
プロフェッショナルサービス
OpenTextは、エンドツーエンドのソリューション導入と包括的なテクノロジーサービスを組み合わせて、システムの改善を支援します。
- 認定専門家と連携して情報管理を近代化プロフェッショナルサービス
- 情報管理ソリューションのタイムトゥーバリューの短縮パッケージサービス
Resources
-
Agentic AST is the category Gartner defines for AI-agent-driven code analysis. Rather than matching rules or tracing a data path, AI agents reason about your source code the way an expert reviewer would, following logic and intent to find vulnerabilities rules-based analysis can't reach. Fortify Agentic Analyzer applies this to your codebase to uncover flawed authorization design, business-logic weaknesses, and subtle injection and persistence patterns. It complements Fortify SAST, which runs a suite of deterministic analyzers fast enough to use on every build.
-
No. It complements SAST, it does not replace it. Fortify SAST stays your fast, broad, deterministic first line of defense on every build, covering a wide range of weakness classes. Fortify Agentic Analyzer adds a deeper, agentic pass you run selectively on higher-risk applications, the way you would schedule a penetration test. Used together, they cover ground neither reaches alone.
-
Yes. It is included under your existing Fortify SAST license at no additional charge. If an application is licensed for SAST analysis, you can analyze it with agentic analysis too, whether you connect through Fortify Software Security Center or Fortify on Demand. You bring your own LLM and pay your provider for usage: there is no separate SKU and no fixed AI surcharge from OpenText.
-
The flaws that turn on logic and intent rather than a traceable data path: broken authorization and authentication design, business-logic weaknesses, and subtle injection and persistence patterns. In a published study across 10 languages, Fortify Agentic Analyzer found 10 of 12 real-world CVEs, most rated CVSS 9.0 or higher, all disclosed after the analysis model's training cutoff, so the results reflect reasoning about the code rather than recall of a known bug.
-
You bring your own. Fortify Agentic Analyzer works with a wide set of LLM providers, connected through your own API key or a supported subscription, so you control model choice and cost. Usage is billed by your provider, not by OpenText. You can select the model and effort level for each stage of a scan to balance depth against spend.
-
They are distinct Fortify capabilities. Fortify Agentic Analyzer finds vulnerabilities rules-based analysis can't reach. Fortify Remediation Aviator triages findings and generates fixes to speed remediation. Fortify Agentic Analyzer does not require Remediation Aviator (which is an add-on). Fortify Agentic Analyzer is included with Fortify SAST.
-
Findings appear in Fortify Software Security Center and Fortify on Demand, reported in the Fortify taxonomy alongside your SAST, DAST, and SCA results, so agentic findings live in the same system of record your team already uses. Findings are deduplicated against your existing SAST results, so you review only what's net-new, and output is also available as SARIF for downstream tools.
-
Because you bring your own LLM, you control the spend. Set a per-run cost cap, choose the model and effort level for each stage, and run agentic analysis where it earns its keep: deeper on your critical applications, lighter elsewhere. There is no fixed AI surcharge from OpenText on top of your provider usage.


