OpenText인 이유
OpenText인 이유
개요OpenText인 이유
OpenText는 수십 년간의 전문 지식을 통해 데이터를 활용하고, 사람과 프로세스를 연결하며, 신뢰할 수 있는 AI를 강화합니다
데이터 관리 및 연결
기업 전체의 데이터를 매끄럽게 통합하여 정보 단절을 없애고, 협업을 강화하며, 리스크를 최소화하세요
AI가 활용 가능한 정보
데이터를 AI가 활용 가능하고 구조화되고, 접근 가능한, 최적화된 정보로 변환하세요
내장 보안 및 규정 준수
규제 및 준수 요구 사항을 충족하고 정보의 수명 주기 전반에 걸쳐 보호하세요
직원 역량 강화
개요직원 역량 강화
OpenText는 사람들이 콘텐츠를 관리하고, 작업을 자동화하며, AI를 사용하고, 협업하여 생산성을 높일 수 있도록 지원합니다
고객
전 세계 수천 개의 기업이 OpenText의 혁신적인 솔루션으로 성공을 거두고 있는 방법을 확인해 보세요
직원
직원은 OpenText의 가장 큰 자산으로, OpenText 브랜드와 가치의 생명입니다.
기업의 사회적 책임
OpenText가 사회적 목표를 발전시키고 긍정적인 변화를 가속화하기 위해 어떤 노력을 하고 있는지 알아보세요
파트너
디지털 혁신을 이루기 최적인 솔루션과 전문성을 갖춘 OpenText 파트너를 만나보세요
AI 리더십
개요Aviator AI
새로운 방식으로 정보 보기
OpenText™ Aviator™
비즈니스, 데이터 및 목표를 파악하는 AI
OpenText™ Content Aviator™
AI 콘텐츠 관리 및 지능형 AI 콘텐츠 어시스턴트를 통해 효율적으로 작업하세요.
OpenText™ Service Management Aviator™
사용자, 서비스 상담원 및 IT 직원이 필요한 답을 찾을 수 있도록 권한을 부여하세요.
OpenText™ Software Delivery Aviator™
더 빠른 앱 제공, 개발 및 자동화된 소프트웨어 테스트를 만나보세요.
OpenText™ Trading Grid™ Aviator™
공급망 전반에서 AI 기반 지식, 인사이트, 안내형 조치를 지금 바로 실현하세요
Aviator AI
개요Aviator AI
새로운 방식으로 정보 보기
OpenText™ Aviator™
비즈니스, 데이터 및 목표를 파악하는 AI
OpenText™ Content Aviator™
AI 콘텐츠 관리 및 지능형 AI 콘텐츠 어시스턴트를 통해 효율적으로 작업하세요.
OpenText™ Service Management Aviator™
사용자, 서비스 상담원 및 IT 직원이 필요한 답을 찾을 수 있도록 권한을 부여하세요.
OpenText™ Software Delivery Aviator™
더 빠른 앱 제공, 개발 및 자동화된 소프트웨어 테스트를 만나보세요.
OpenText™ Trading Grid™ Aviator™
공급망 전반에서 AI 기반 지식, 인사이트, 안내형 조치를 지금 바로 실현하세요
비즈니스 네트워크
개요Business Network
한 번만 연결하면 안전한 B2B 통합 플랫폼으로 모든 대상과 연결할 수 있습니다.
콘텐츠
개요Content
AI가 활용 가능한 콘텐츠 관리 솔루션으로 지식 재구성
사이버 보안
개요Cybersecurity
기업 보호를 위한 통합 사이버 보안 솔루션
애플리케이션 전송 관리
개요Application Delivery Management
AI 기반 DevOps 자동화, 테스트 및 품질을 통해 더 나은 소프트웨어를 더 빠르게 제공
관측 가능성 및 서비스 관리
개요Observability and Service Management
IT 운영의 비용과 복잡성을 줄이기 위해 필요한 명확성 확보
API
개요APIs
통합, 자동화 및 맞춤형 경험을 구축하여 OpenText 솔루션의 가치를 확장하세요
OpenText™ API Services
사용자 정의 애플리케이션 및 워크플로를 지원하는 실시간 정보 흐름을 제공하는 OpenText Cloud API를 사용하여 원하는 방식으로 구축
Device and Data Protection
개요Device and Data Protection
중요한 데이터를 보호하고 중요한 순간에 복구하기
신뢰할 수 있는 데이터 및 AI
개요신뢰할 수 있는 데이터 및 AI
안전한 정보 관리가 신뢰할 수 있는 AI를 만나다
OpenText™ Aviator™ Studio
데이터 언어로 에이전트를 구축, 배포 및 반복할 수 있는 공간
OpenText™ Discovery
AI를 강화하기 위해 데이터 수집 및 메타데이터 태그 지정 자동화를 지원하는 도구 세트
OpenText™ Data Compliance
거버넌스를 사전 예방적이고 지속 가능하게 만드는 서비스 및 API 제품군
OpenText™ Aviator™ AI 서비스
AI 여정을 도와주는 전문 서비스 전문가
인공 지능
개요Aviator AI
새로운 방식으로 정보 보기
OpenText™ Aviator™
비즈니스, 데이터 및 목표를 파악하는 AI
OpenText™ Content Aviator™
AI 콘텐츠 관리 및 지능형 AI 콘텐츠 어시스턴트를 통해 효율적으로 작업하세요.
OpenText™ Service Management Aviator™
사용자, 서비스 상담원 및 IT 직원이 필요한 답을 찾을 수 있도록 권한을 부여하세요.
OpenText™ Software Delivery Aviator™
더 빠른 앱 제공, 개발 및 자동화된 소프트웨어 테스트를 만나보세요.
OpenText™ Trading Grid™ Aviator™
공급망 전반에서 AI 기반 지식, 인사이트, 안내형 조치를 지금 바로 실현하세요

클라우드 파트너
개요클라우드 파트너
OpenText는 주요 클라우드 인프라 제공업체와 협력하여 어디서나 OpenText 솔루션을 실행할 수 있는 유연성을 제공합니다
엔터프라이즈 애플리케이션 파트너
개요엔터프라이즈 애플리케이션 파트너
OpenText는 최고의 엔터프라이즈 앱 제공업체와 협력하여 비정형 데이터를 활용함으로써 더 나은 비즈니스 인사이트를 제공합니다
에이전틱 애플리케이션 보안
규칙 기반 분석으로는 찾을 수 없는 취약점을 Fortify Agentic Analyzer로 발견
개요

주요 이점
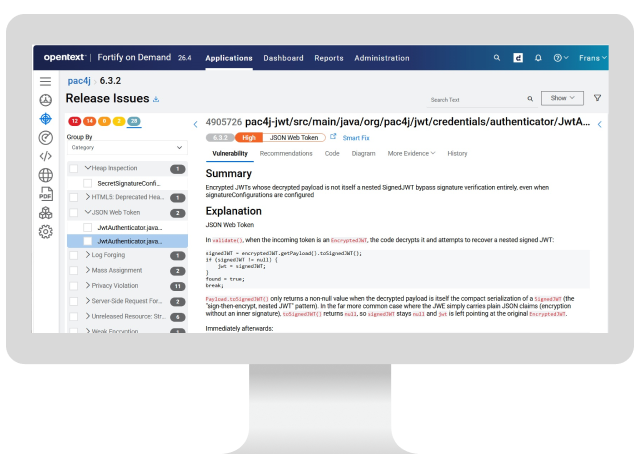
현재 운영 중인 Fortify 워크플로를 벗어나지 않고도 규칙 기반 분석이 놓치는 취약점을 찾아내세요.
-

규칙 기반 분석이 닿지 못하는 치명적인 결함 탐지
에이전틱 분석은 10개 언어에 걸친 실제 치명적 CVE 12건 중 10건을 탐지합니다. 이들은 추적할 오염 데이터 경로가 없는 로직 및 권한 부여 버그로, 대부분 CVSS 9.0 이상 등급입니다.
-

모든 탐지 결과를 한곳에서 관리
탐지 결과는 규칙 기반 SAST 결과와 대조해 중복이 제거되고, Fortify 범주에 매핑된 후 Fortify Software Security Center와 Fortify on Demand에 표시됩니다. 별도의 도구도, 별도의 트리아지 대기열도 필요하지 않습니다.
-

새 SKU 없이 심층 에이전틱 분석 추가
Fortify Agentic Analyzer는 기존 Fortify SAST 라이선스에 포함되어 있습니다. 지원되는 공급업체 중 원하는 곳의 LLM을 직접 연결해 사용하고, 사용량에 대한 비용은 해당 공급업체에만 지불하세요.
비즈니스 영향
-
로직 및 권한 부여 결함 탐지
일부 결함은 추적할 데이터 흔적을 남기지 않습니다. 하드코딩된 비밀번호로 오인된 메시지 문자열과 같은 오탐을 제거하고, 규칙 기반 분석으로는 추적할 수 없는 로직 및 권한 부여 결함을 찾아내세요.
-
고위험 앱을 위한 심층 커버리지
침투 테스트 일정을 잡듯 중요 앱에 대해 정기적으로 에이전틱 분석을 실행하고, SAST는 빠르고 일상적인 1차 방어선으로 계속 활용하세요.
-
신규 탐지 결과만 제공
팀은 SAST가 이미 찾아낸 문제를 다시 트리아지하느라 시간을 낭비합니다. SAST 결과를 입력하면 Fortify Agentic Analyzer가 해당 항목을 제외하므로, 팀은 새로운 항목만 검토하면 됩니다.
-
단일 기록 시스템
탐지 결과는 Fortify 분류 체계에 따라 Fortify Software Security Center와 Fortify on Demand에 전달되고 SARIF 형식으로 내보낼 수 있어, 에이전틱 분석 결과를 나머지 AppSec 프로그램과 함께 관리할 수 있습니다.
-
스캔 비용 관리
원하는 LLM을 연결해 사용하므로 비용을 직접 관리할 수 있습니다. 실행당 비용 한도를 설정하고, 단계별로 모델과 분석 강도를 선택하며, 중요 앱은 더 깊게, 그 외 앱은 더 가볍게 분석하세요.
솔루션의 구성 요소 살펴보기
제품
OpenText는 에이전틱 분석과 규칙 기반 분석을 하나의 애플리케이션 보안 프로그램으로 통합합니다. Fortify Agentic Analyzer(SAST에 포함)는 규칙 기반 분석이 찾지 못하는 문제를 찾아내고, Fortify SAST는 빠르고 결정론적인 커버리지를 제공하며, Fortify on Demand는 이 모든 것을 SaaS 형태로 제공합니다.
- OpenText™ Fortify™ SAST업계 최고의 정확도로 보안 문제를 조기에 찾아 해결하세요
- OpenText™ Fortify™ Remediation Aviator™결함이 아닌 코드 수정을 보여주는 AI로 소음에서 결과로 전환하기
- OpenText™ Fortify™ on Demand보안 테스트, 취약성 관리, 맞춤형 전문 지식 및 지원을 활용합니다
- 엔터프라이즈 애플리케이션 보안 플랫폼개발자를 지원하고, 보안을 강화하고, 더 빠르게 배송하세요.
전문 서비스
OpenText는 종단 간 솔루션 구현과 포괄적인 기술 서비스를 결합하여 시스템 개선을 지원합니다.
- 인증된 전문가와 함께 정보 관리를 현대화하세요전문 서비스
- 정보 관리 솔루션의 가치 실현 시간 단축패키지드 서비스
Resources
-
Agentic AST is the category Gartner defines for AI-agent-driven code analysis. Rather than matching rules or tracing a data path, AI agents reason about your source code the way an expert reviewer would, following logic and intent to find vulnerabilities rules-based analysis can't reach. Fortify Agentic Analyzer applies this to your codebase to uncover flawed authorization design, business-logic weaknesses, and subtle injection and persistence patterns. It complements Fortify SAST, which runs a suite of deterministic analyzers fast enough to use on every build.
-
No. It complements SAST, it does not replace it. Fortify SAST stays your fast, broad, deterministic first line of defense on every build, covering a wide range of weakness classes. Fortify Agentic Analyzer adds a deeper, agentic pass you run selectively on higher-risk applications, the way you would schedule a penetration test. Used together, they cover ground neither reaches alone.
-
Yes. It is included under your existing Fortify SAST license at no additional charge. If an application is licensed for SAST analysis, you can analyze it with agentic analysis too, whether you connect through Fortify Software Security Center or Fortify on Demand. You bring your own LLM and pay your provider for usage: there is no separate SKU and no fixed AI surcharge from OpenText.
-
The flaws that turn on logic and intent rather than a traceable data path: broken authorization and authentication design, business-logic weaknesses, and subtle injection and persistence patterns. In a published study across 10 languages, Fortify Agentic Analyzer found 10 of 12 real-world CVEs, most rated CVSS 9.0 or higher, all disclosed after the analysis model's training cutoff, so the results reflect reasoning about the code rather than recall of a known bug.
-
You bring your own. Fortify Agentic Analyzer works with a wide set of LLM providers, connected through your own API key or a supported subscription, so you control model choice and cost. Usage is billed by your provider, not by OpenText. You can select the model and effort level for each stage of a scan to balance depth against spend.
-
They are distinct Fortify capabilities. Fortify Agentic Analyzer finds vulnerabilities rules-based analysis can't reach. Fortify Remediation Aviator triages findings and generates fixes to speed remediation. Fortify Agentic Analyzer does not require Remediation Aviator (which is an add-on). Fortify Agentic Analyzer is included with Fortify SAST.
-
Findings appear in Fortify Software Security Center and Fortify on Demand, reported in the Fortify taxonomy alongside your SAST, DAST, and SCA results, so agentic findings live in the same system of record your team already uses. Findings are deduplicated against your existing SAST results, so you review only what's net-new, and output is also available as SARIF for downstream tools.
-
Because you bring your own LLM, you control the spend. Set a per-run cost cap, choose the model and effort level for each stage, and run agentic analysis where it earns its keep: deeper on your critical applications, lighter elsewhere. There is no fixed AI surcharge from OpenText on top of your provider usage.


