Why OpenText
Why OpenText
OverviewWhy OpenText
OpenText brings decades of expertise to help you unlock data, connect people and processes, and fuel AI with trust
Manage and connect data
Unify data seamlessly across your enterprise to eliminate silos, improve collaboration, and reduce risks
AI-ready information
Get AI-ready and transform your data into structured, accessible, optimized information
Built-in security and compliance
Meet regulatory and compliance requirements and protect your information throughout its lifecycle
Empowering people
OverviewEmpowering people
OpenText helps people manage content, automate work, use AI, and collaborate to boost productivity
Customers
See how thousands of companies around the world are succeeding with innovative solutions from OpenText
Employees
Our people are our greatest asset; they are the life of the OpenText brand and values
Corporate Responsibility
Learn how we aspire to advance societal goals and accelerate positive change
Partners
Find a highly skilled OpenText partner with the right solution to enable digital transformation
Deploy anywhere
OverviewDeployment options
Explore scalable and flexible deployment options for global organizations of any size
Sovereign cloud
Local control. Global scale. Trusted AI
Private cloud
Unlock the value of the cloud while maintaining control and compliance
On-premises
Maintain full control of your data on your own infrastructure
Public cloud
Protect, scale, and use business information in your cloud of choice
AI leadership
OverviewAviator AI
See information in new ways
OpenText™ Aviator™
AI that understands your business, your data, and your goals
OpenText™ Content Aviator™
Power work with AI content management and an intelligent AI content assistant
OpenText™ Service Management Aviator™
Empower users, service agents, and IT staff to find the answers they need
OpenText™ Software Delivery Aviator™
Enable faster app delivery, development, and automated software testing
OpenText™ Trading Grid™ Aviator™
Unlock AI-powered knowledge, insights, and guided action across your supply chain
OpenText™ Aviator™ Studio
A place where you can build, deploy, and iterate on agents in your data's language
Aviator AI
OverviewAviator AI
See information in new ways
OpenText™ Aviator™
AI that understands your business, your data, and your goals
OpenText™ Content Aviator™
Power work with AI content management and an intelligent AI content assistant
OpenText™ Service Management Aviator™
Empower users, service agents, and IT staff to find the answers they need
OpenText™ Software Delivery Aviator™
Enable faster app delivery, development, and automated software testing
OpenText™ Trading Grid™ Aviator™
Unlock AI-powered knowledge, insights, and guided action across your supply chain
OpenText™ Aviator™ Studio
A place where you can build, deploy, and iterate on agents in your data's language
Business Network
OverviewBusiness Network
Connect once, reach anything with a secure B2B integration platform
Content
OverviewContent
Reimagine knowledge with AI-ready content management solutions
OpenText™ Content Aviator™(AI)
Supercharge intelligent workspaces with AI to modernize work
Cybersecurity
OverviewCybersecurity
Integrated cybersecurity solutions for enterprise protection
DevOps
OverviewDevOps
Ship better software—faster—with AI-driven DevOps automation, testing, and quality
OpenText™ Software Delivery Aviator™(AI)
Elevate millions of developers with AI-powered DevOps experiences
Experience and Fax
OverviewExperience and Fax
Reimagine conversations with unforgettable customer experiences
Legal Tech
OverviewLegal Tech
Make smarter decisions with AI-powered legal software and services
Observability and Service Management
OverviewObservability and Service Management
Get the clarity needed to cut the cost and complexity of IT operations
OpenText™ Service Management Aviator™(AI)
Redefine Tier 1 business support functions with self-service capabilities from private generative AI
APIs
OverviewAPIs
Extend the value of your OpenText solutions by building integrations, automation and custom experiences
OpenText™ API Services
Build it your way with OpenText Cloud APIs that create the real-time information flows that enable custom applications and workflows
Device and Data Protection
OverviewDevice and Data Protection
Protect what matters, recover when it counts
Solutions
Trusted Data & AI
OverviewTrusted Data & AI
Secure information management meets trusted AI
OpenText™ Aviator™ Studio
A place where you can build, deploy, and iterate on agents in your data's language
OpenText™ Discovery
A set of tools to help ingest data and automate metadata tagging to fuel AI
OpenText™ Data Compliance
A suite of services and APIs that make governance proactive and persistent
OpenText™ Aviator™ AI Services
Professional services experts who help you on your AI journey
Information Reimagined
OverviewInformation Reimagined
Get greater visibility and sharper insights from AI-driven information management. Ready to see how?
Knowledge reimagined
Transform daily work with enterprise content management powered by AI
Service Management reimagined
Cut the cost and complexity of IT service management, AIOps, and observability
Connections reimagined
AI-powered B2B integration for supply chain success
Conversations reimagined
Drive value, growth, and loyalty with connected customer experiences
Engineering reimagined
Agile development and software delivery? It only seems impossible
Security reimagined
Cybersecurity for the Enterprise
Decisions reimagined
Unlock insights with AI data analytics
Artificial Intelligence
OverviewAviator AI
See information in new ways
OpenText™ Aviator™
AI that understands your business, your data, and your goals
OpenText™ Content Aviator™
Power work with AI content management and an intelligent AI content assistant
OpenText™ Service Management Aviator™
Empower users, service agents, and IT staff to find the answers they need
OpenText™ Software Delivery Aviator™
Enable faster app delivery, development, and automated software testing
OpenText™ Trading Grid™ Aviator™
Unlock AI-powered knowledge, insights, and guided action across your supply chain
OpenText™ Aviator™ Studio
A place where you can build, deploy, and iterate on agents in your data's language
Industry
OverviewIndustry solutions
Improve efficiency, security, and customer satisfaction with OpenText
Energy and resources
Transform energy and resources operations with cloud, cybersecurity, and AI
Financial services
Boost customer experience, compliance, and efficiency with AI
Government
Reimagine your mission with government-secure information management
Healthcare and life sciences
Improve care delivery and patient engagement with AI-powered solutions
Legal
Modernize legal teams with automated, AI-powered legal tech solutions
Manufacturing
Modernize manufacturing operations and logistics to reduce costs and ensure compliance
Retail and consumer goods
Enhance consumer engagement with omnichannel retail solutions and AI
Enterprise Application
OverviewSolutions for Enterprise Applications
Run processes faster and with less risk
Maximize sustained growth, value, and innovation with intelligent enterprise solutions from OpenText and SAP
Optimize Salesforce effectiveness by bringing together transactional data and unstructured content
Services
Services
OverviewServices
Accelerate digital transformation with guidance from certified experts
Professional Services
Modernize your information management with certified experts
Customer Success Services
Meet business goals with expert guidance, managed services, and more
Support Services
Turn support into your strategic advantage
Managed Services
Free up your internal teams with expert IT service management
Learning Services
Discover training options to help users of all skill levels effectively adopt and use OpenText products
Professional Services
OverviewProfessional Services
Modernize your information management with certified experts
Customer Success Services
OverviewCustomer Success Services
Meet business goals with expert guidance, managed services, and more
Support Services
OverviewSupport Services
Turn support into your strategic advantage
Managed Services
OverviewManaged Services
Free up your internal teams with expert IT service management
Learning Services
OverviewLearning Services
Discover training options to help users of all skill levels effectively adopt and use OpenText products
Partners
Find a Partner
OverviewFind a partner
Find a highly skilled OpenText partner with the right solution to enable digital transformation

Cloud Partners
OverviewCloud Partners
OpenText partners with leading cloud infrastructure providers to offer the flexibility to run OpenText solutions anywhere
Optimize performance and reduce costs with applications deployed on a secure, globally scaled platform
Accelerate migration and modernization with deployment in a highly secure and compliant public cloud
Enterprise Application Partners
OverviewEnterprise Application Partners
OpenText partners with top enterprise app providers to unlock unstructured content for better business insights
Maximize sustained growth, value, and innovation with intelligent enterprise solutions from OpenText and SAP
Optimize Salesforce effectiveness by bringing together transactional data and unstructured content
Partner Solutions
OverviewPartner Solutions
Discover flexible and innovative offerings designed to add value to OpenText solutions
Resources for Partners
OverviewResources for Partners
Discover the resources available to support and grow Partner capabilities
Support
OverviewCustomer Support
Get expert product and service support to accelerate issue resolution and keep business flows running efficiently
Resources
OverviewResources
Explore detailed services and consulting presentations, briefs, documentation and other resources
Choose your region:
Europe, Middle East and Africa
Asia–Pacific
Agentic application security
Find what rules-based analysis can’t with Fortify Agentic Analyzer
Overview

Key benefits
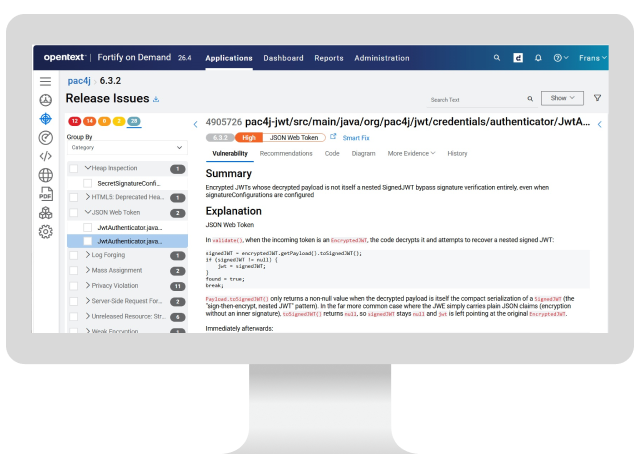
Catch vulnerabilities rules-based analysis misses, without leaving the Fortify workflow you already run.
-

Find the critical flaws rules-based analysis can’t reach
Agentic analysis catches 10 of 12 real critical CVEs across 10 languages, most rated CVSS 9.0 or higher—the logic and authorization bugs where there is no tainted data path to trace.
-

Manage all your findings in one place
Findings are deduplicated against your rules-based SAST results, mapped to Fortify categories, and shown in Fortify Software Security Center and Fortify on Demand. No second tool, no second triage queue is required.
-

Add agentic depth with no new SKU
Fortify Agentic Analyzer is included under your existing Fortify SAST license. Bring your own LLM from any supported provider and pay only your provider for usage.
Business impacts
-
Logic and authorization flaw detection
Some flaws leave no data trail to follow. Clear false positives, like a message string mistaken for a hard-coded password, and surface the logic and authorization flaws rules-based analysis can't trace.
-
Deeper coverage for high-risk apps
Run agentic analysis periodically on your critical apps, the way you would schedule a penetration test, while SAST stays your fast, daily first line of defense.
-
Net-new findings only
Teams lose time re-triaging issues SAST already found. Pass your SAST results in and Fortify Agentic Analyzer drops them, so your team reviews only what's net-new.
-
One system of record
Findings land in Fortify Software Security Center and Fortify on Demand in the Fortify taxonomy and export as SARIF, so agentic results live alongside the rest of your AppSec program.
-
Scan cost control
You bring your own LLM, so you control the spend. Set a per-run cost cap, choose the model and effort for each stage, and run deeper on critical apps, lighter elsewhere.
Explore the components of the solution
Products
OpenText brings agentic and rules-based analysis together in one application security program. Fortify Agentic Analyzer (included with SAST) finds what rules-based analysis can’t; Fortify SAST provides fast, deterministic coverage; and Fortify on Demand delivers it as SaaS.
- OpenText™ Fortify™ SASTFind and fix security issues early with industry-leading accuracy
- OpenText™ Fortify™ Remediation Aviator™Move from noise to outcomes with AI that shows the code fix, not just the flaw
- OpenText™ Fortify™ on DemandUnlock security testing, vulnerability management, and tailored expertise and support
- Enterprise application security platformEnable developers. Strengthen security. Accelerate delivery
Professional Services
OpenText combines end-to-end solution implementation with comprehensive technology services to help improve systems.
- Modernize your information management with certified expertsProfessional services
- Reduce time-to-value of Information Management solutionsPackaged Services
Resources
-
Agentic AST is the category Gartner defines for AI-agent-driven code analysis. Rather than matching rules or tracing a data path, AI agents reason about your source code the way an expert reviewer would, following logic and intent to find vulnerabilities rules-based analysis can't reach. Fortify Agentic Analyzer applies this to your codebase to uncover flawed authorization design, business-logic weaknesses, and subtle injection and persistence patterns. It complements Fortify SAST, which runs a suite of deterministic analyzers fast enough to use on every build.
-
No. It complements SAST, it does not replace it. Fortify SAST stays your fast, broad, deterministic first line of defense on every build, covering a wide range of weakness classes. Fortify Agentic Analyzer adds a deeper, agentic pass you run selectively on higher-risk applications, the way you would schedule a penetration test. Used together, they cover ground neither reaches alone.
-
Yes. It is included under your existing Fortify SAST license at no additional charge. If an application is licensed for SAST analysis, you can analyze it with agentic analysis too, whether you connect through Fortify Software Security Center or Fortify on Demand. You bring your own LLM and pay your provider for usage: there is no separate SKU and no fixed AI surcharge from OpenText.
-
The flaws that turn on logic and intent rather than a traceable data path: broken authorization and authentication design, business-logic weaknesses, and subtle injection and persistence patterns. In a published study across 10 languages, Fortify Agentic Analyzer found 10 of 12 real-world CVEs, most rated CVSS 9.0 or higher, all disclosed after the analysis model's training cutoff, so the results reflect reasoning about the code rather than recall of a known bug.
-
You bring your own. Fortify Agentic Analyzer works with a wide set of LLM providers, connected through your own API key or a supported subscription, so you control model choice and cost. Usage is billed by your provider, not by OpenText. You can select the model and effort level for each stage of a scan to balance depth against spend.
-
They are distinct Fortify capabilities. Fortify Agentic Analyzer finds vulnerabilities rules-based analysis can't reach. Fortify Remediation Aviator triages findings and generates fixes to speed remediation. Fortify Agentic Analyzer does not require Remediation Aviator (which is an add-on). Fortify Agentic Analyzer is included with Fortify SAST.
-
Findings appear in Fortify Software Security Center and Fortify on Demand, reported in the Fortify taxonomy alongside your SAST, DAST, and SCA results, so agentic findings live in the same system of record your team already uses. Findings are deduplicated against your existing SAST results, so you review only what's net-new, and output is also available as SARIF for downstream tools.
-
Because you bring your own LLM, you control the spend. Set a per-run cost cap, choose the model and effort level for each stage, and run agentic analysis where it earns its keep: deeper on your critical applications, lighter elsewhere. There is no fixed AI surcharge from OpenText on top of your provider usage.


